Back to all blogs
CMS

18 Essential Security Steps to Protect Your CMS Website from Cyber Threats

REEA Digital Team6 min read
Share:
18 Essential Security Steps to Protect Your CMS Website from Cyber Threats

Content Management Systems (CMS) like WordPress, Drupal, and Joomla have transformed how organizations build and manage digital platforms. While their open-source ecosystems make it easy for teams to publish content without writing code, their widespread adoption also makes unpatched installations frequent targets for automated attacks. Below are 18 essential security practices to harden your CMS against modern cyber threats.

1. Update Regularly

Keeping your CMS theme, extensions, and core updated is essential for security hygiene.

Core Updates: Always install the latest version of core CMS packages.
Plugin and Theme Updates: Keep plugins, extensions, and themes updated to eliminate known security vulnerabilities.
Remove Unused Add-ons: Delete inactive themes and plugins to reduce your attack surface.

2. Enforce Strong Passwords

Weak or predictable passwords make CMS administrative accounts prime targets for brute-force attacks.

Complex Passwords: Enforce passwords using a mix of uppercase letters, numbers, and symbols.
Two-Factor Authentication (2FA): 2FA adds an essential second defense layer even if credentials are leaked.
Password Management: Use enterprise password managers to generate and store unique credentials securely.

3. Limit User Permissions

Limit administrative access based strictly on role responsibilities to minimize exposure.

Least Privilege Principle: Grant users only the minimum permissions necessary for their daily work.
Access Audits: Regularly audit user accounts and revoke permissions for inactive team members.

4. Protect Login Pages

Default administrative login endpoints are the primary target for automated credential-stuffing and brute-force attacks.

Custom Login URL: Change or restrict access to default admin URLs (such as /wp-admin) to block automated bot scans.
Limit Login Attempts: Enforce rate limiting and temporary IP lockouts after repeated failed login attempts.
CAPTCHA Protection: Enable reCAPTCHA or Cloudflare Turnstile on login and registration forms to filter out bots.

5. Use HTTPS for Security

SSL/TLS encryption increases security of your data transfer between your user and site.
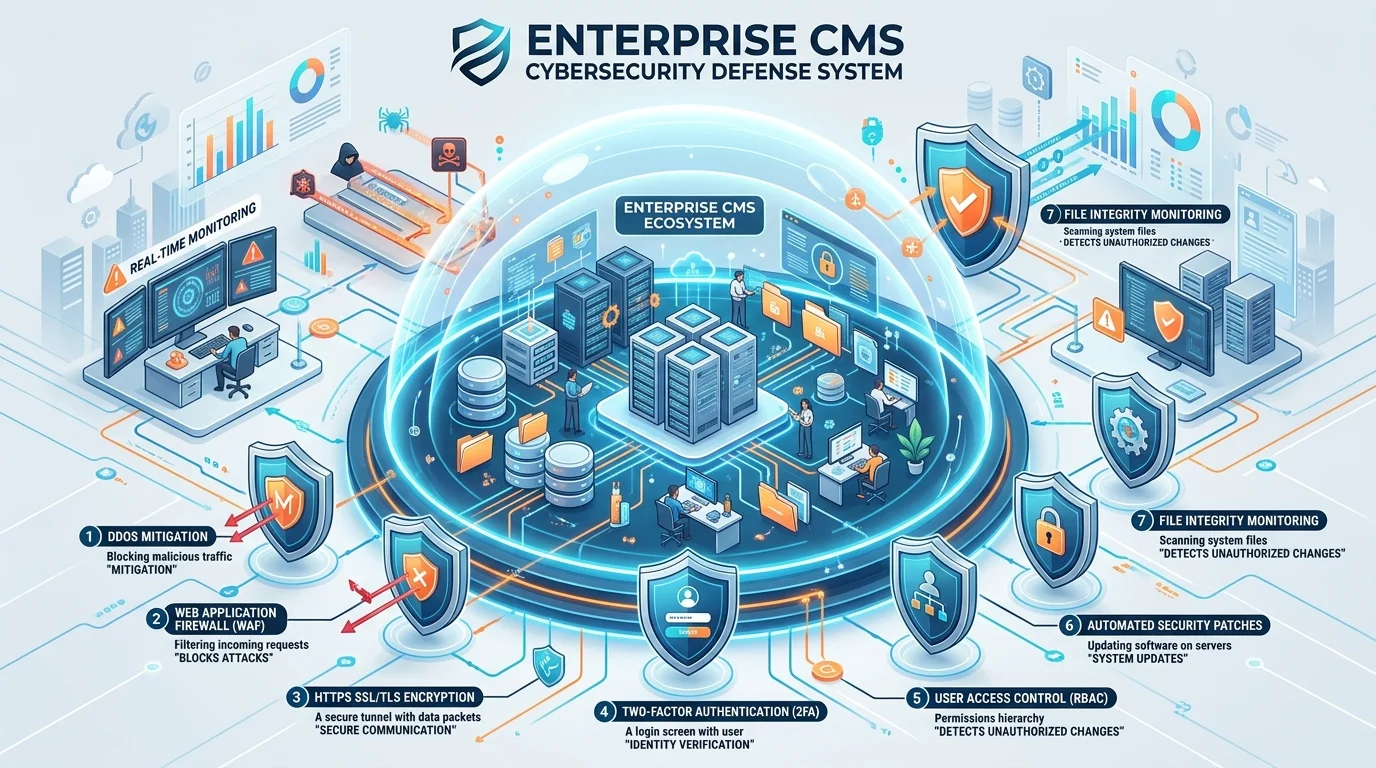
Enterprise CMS Cybersecurity Defense System: Multi-Layered Protection, WAF, 2FA, SSL Encryption, and Threat Monitoring
SSL Certificates: We recommend installing a valid SSL certificate for encryption of your data and secure connections.
Always-On SSL: Enforce HTTPS sitewide to safeguard sensitive data and prevent eavesdropping.

6. Use a Web Application Firewall (WAF)

A Web Application Firewall inspects incoming HTTP traffic at the edge and blocks malicious requests before they reach your CMS server.

Protection Against Exploits: Filters out SQL injection (SQLi), cross-site scripting (XSS), and malicious bot payloads.
Cloud-Based Edge Filtering: Cloud WAFs (such as Cloudflare or AWS WAF) deploy quickly at the DNS layer without adding load to your origin server.

7. Backup Your Site

Websites can be restored quickly following an incident if backups are frequent and reliable.

Automated Backups: Implement automated daily backups of both database records and server files.
Secure Backup Storage: Store encrypted backup copies on isolated, offsite cloud storage.
Restore Testing: Regularly test your backup restoration process to guarantee swift recovery without data loss.

8. Control File Permissions

Strict server file permissions prevent unauthorized users or compromised processes from modifying critical configuration files.

Restrict Configuration Access: Disable file editing from the CMS dashboard and lock down sensitive files like wp-config.php or settings.php.
Recommended Permission Settings: Set standard directory permissions to 755 and file permissions to 644 (with stricter 600 or 440 permissions on configuration secrets).
Disable Directory Browsing: Disable directory indexing on your web server so visitors cannot browse folder contents.

9. Secure the Database

Because the CMS database stores user records, configuration settings, and content, hardening database access is just as important as securing application files.

Change Default Table Prefixes: Replace default table prefixes (such as wp_) during setup to mitigate automated SQL injection scripts.
Database Access Controls: Use strong, unique database credentials and restrict database network access strictly to the application host.
Regular Database Backups: Schedule automated, encrypted database snapshots alongside file backups.

10. Use Security Plugins

Major CMS ecosystems offer dedicated security modules and plugins that add endpoint firewall rules, login hardening, and integrity monitoring.

WordPress Security Suites: Proven options include Wordfence, Patchstack, Solid Security, and Sucuri.
Drupal & Joomla Security Modules: Enable contributed hardening modules such as Security Kit (Seckit), Paranoia, and automated vulnerability advisories.
Real-Time File Integrity: Configure automated alerts when core files or active plugins are modified unexpectedly.

11. Malware Scanning and Removal

Scan your website files regularly to detect injected scripts and unauthorized changes.

Automated Scanning Tools: Use automated security tools to detect malware and file integrity issues.
Manual Inspections: Use version control to track file changes and verify unexpected modifications.
Quick Incident Response: Quarantine and restore infected files immediately to minimize exposure.

12. Disable XML-RPC (If Unneeded)

Legacy remote-publishing protocols like xmlrpc.php in WordPress are frequently abused for amplified brute-force and DDoS pingback attacks.

Disable Unused Endpoints: Block xmlrpc.php at the web server or WAF level unless a specific legacy integration requires it.
Use Modern REST APIs with Auth: Prefer scoped REST API tokens or Application Passwords over legacy XML-RPC connections.

13. Add Security Headers

HTTP security headers provide essential defense against common web vulnerabilities.

Content Security Policy (CSP): Controls resource loading to safeguard your website from cross-site scripting (XSS).
X-Frame-Options: Prevents iframe embedding, protecting your visitors from clickjacking attacks.
X-Content-Type-Options: Prevents MIME-sniffing, ensuring browsers interpret files strictly as intended.

14. Conduct Security Audits

Proactive security assessments identify misconfigurations and vulnerable dependencies before attackers can exploit them.

Penetration Testing: Engage security specialists periodically to test custom themes, plugins, and API endpoints.
Vulnerability Scanners: Run automated dependency and OWASP vulnerability scans as part of your release workflow.

15. Monitor for Unusual Activity

Continuous observability across administrative actions and server logs allows teams to detect and contain suspicious behavior early.

Audit & Activity Logs: Maintain immutable logs of user logins, privilege changes, plugin installations, and content edits.
Real-Time Anomaly Alerts: Configure automated notifications for repeated failed logins, new admin account creation, or unauthorized file changes.

16. Choose Secure Hosting

Your hosting infrastructure is the foundation of your CMS security posture.

Managed Enterprise Hosting: Choose reputable hosting providers that offer OS-level patching, network firewalls, and malware isolation.
Isolated Environments: Prefer containerized, VPS, or dedicated hosting environments over low-cost shared hosting to prevent cross-site contamination.

17. Use a Content Delivery Network (CDN)

A CDN improves page load times while adding an extra layer of perimeter defense.

DDoS Protection: CDNs mitigate malicious traffic and absorb volumetric denial-of-service attacks.
Global Edge Distribution: Distribute cached content globally to reduce server load and latency.

18. Educate Users and Admins

Human error—such as phishing, weak credentials, or installing unvetted plugins—remains a leading cause of CMS compromises.

Security Awareness Training: Train editors, moderators, and administrators to recognize phishing attempts and follow secure publishing workflows.
Governance & Patch Policies: Establish clear internal policies for vetting third-party extensions and applying security updates promptly.

Because open-source CMS platforms power a massive share of the web, proactive defense is essential. Implementing these 18 security measures—combined with automated monitoring and disciplined patching—will significantly reduce your attack surface and keep your digital platform resilient.
Back to all blogs
Share:
LET’S TALK

Let’s discuss your project.

Tell us what you need to build or improve. We’ll discuss your goals and a practical next step.

Request a call

We’ll contact you to arrange a call.