Modern business demands have turned software development into a more sophisticated discipline, one closely tied to the principles of confidentiality, integrity and availability. As cyber threats grow, cybersecurity has to be built into every stage of the software development lifecycle (SDLC). This post covers fourteen essential cybersecurity best practices for protecting custom software from evolving security risks.
1. Why Cybersecurity Matters in Custom Software Development
Custom software is built for a specific client and often handles valuable business data, which makes it an attractive target for attackers. Cybersecurity therefore plays a critical role throughout the software development lifecycle (SDLC). The goal is simple: data must not be altered, sensitive information must not be accessed without authorization, and the application itself must not be compromised by malicious code.
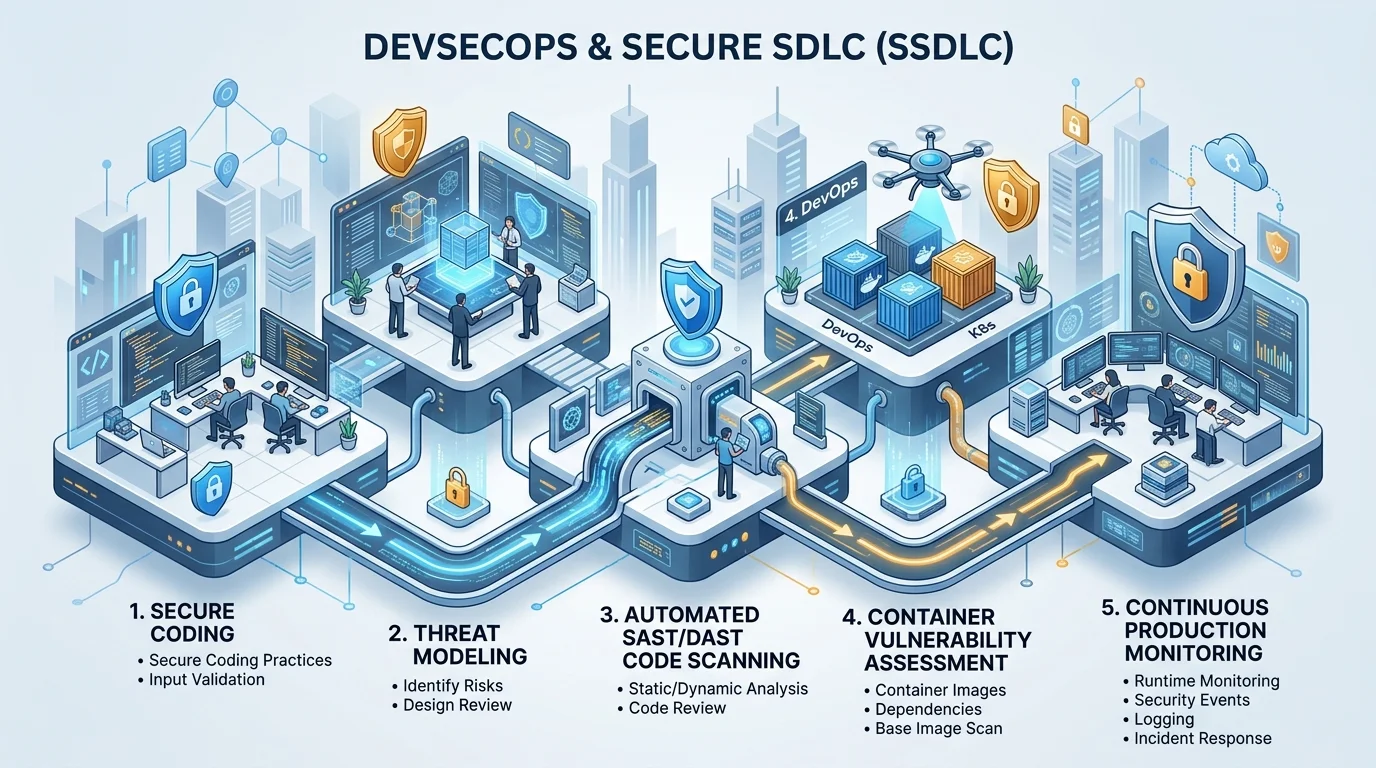
2. Build Security Into Every Stage of Development
In every phase throughout the software development lifecycle, security controls must be proactively embedded. Shift-left security emphasizes addressing vulnerabilities early to minimize remediation cost and risk:
3. Adopt Secure Coding Principles
Secure coding principles help developers greatly reduce the number of vulnerabilities in their code.
Developers should follow established guidance such as the OWASP (Open Web Application Security Project) recommendations or the CERT Secure Coding standards. Key practices include:
4. Choose Secure Development Tools
Use tools that strengthen security during development, such as:
Ensure all security tools and dependencies are updated regularly to the latest versions to mitigate known exploits.
5. Enforce Strong Authentication and Access Control
Authentication and access control are core cybersecurity measures. Best practices include:
6. Vet Third-Party Dependencies
Developers building custom applications often rely on libraries, frameworks and APIs written by others. Reusing external code brings its own risks, so:
Use tools such as Dependabot to identify outdated and vulnerable libraries.
Avoid libraries from untrusted sources.
Keep monitoring third-party code and apply updates as new versions are released.
7. Protect Sensitive Data With Encryption
Encryption protects sensitive information from being accessed or used by unauthorized people. Recommended actions include:
8. Test for Security Regularly
Security testing finds weaknesses that may have been missed during development. It includes:
9. Train Developers and Stakeholders
Everyone has a part to play in keeping information systems secure. Regular training and awareness programs help developers, testers and stakeholders understand their roles. Topics should include:
Current cyber threats and attack vectors
Secure coding and testing principles
Compliance and industry requirements
10. Detect and Respond to Threats
No system is immune to attack, however many best practices you apply. Put proper monitoring and incident response in place so threats are detected and handled quickly.
11. Comply With Security and Privacy Frameworks
Following recognized industry standards and regulations helps protect your software and builds trust with users. Common frameworks include:
Complying with these frameworks shows a clear commitment to protecting user data and to following security best practices.
12. Apply the ‘Never Trust, Always Verify’ Principle
Under a Zero Trust model, every access request is treated as a potential threat, whether it comes from inside or outside the network. The core ideas are:
13. Adopt DevSecOps
DevSecOps builds security into DevOps processes. Key practices include:
14. Plan for Backup and Disaster Recovery
Regular backups and a solid disaster recovery strategy give you confidence that your software can withstand an attack. Best practices include:
Leaving security out of the development process is a failure in custom software development. You can avoid it by embedding security throughout the lifecycle, following secure coding practices and building a security-aware culture. Regular penetration testing after deployment and meeting compliance requirements add further layers of defense.
As technology advances, cybersecurity becomes ever more critical, because greater connectivity increases the risk of attack. These practices help developers build software that is far more resilient to threats.
Fortify Your Software With REEA Digital’s Cybersecurity Expertise
Strengthen your organization with security built into every step of the process.
Today's connected, global software landscape demands an integrated approach to security. At REEA Digital, we focus on security from the very start of a project so your applications are protected against attackers. We build cybersecurity into every stage of the SDLC to protect your organization, its data and its users.
Why Choose REEA Digital for Secure Software Development?
Security built in from the start:
We include security in every development stage, from design through maintenance.
We carry out risk assessments, penetration tests and vulnerability scans.
Standards compliance:
We follow OWASP guidance and the CERT Secure Coding standards.
We help you meet regulations such as HIPAA, GDPR and PCI DSS.
Modern security models:
We apply Zero Trust policies for information access and network segmentation.
We use DevSecOps to keep security in place throughout development.
Our Approach to Cybersecurity
Let’s Build Software That’s Secure by Design
Protect your software against ongoing cyber threats with REEA Digital's secure development services. Contact us today to build custom applications designed with security and robustness in mind.
Schedule a Consultation or Request a Free Quote to learn more about our cybersecurity solutions.
Frequently Asked Questions
Answers to common questions about secure software development.
What are the best practices for cybersecurity in secure software development?
Best practices for cybersecurity in secure software development include implementing regular security assessments, ensuring robust security measures throughout the development process, and adhering to security requirements set by industry standards.
How can a development team ensure security in software development?
A development team can ensure security in software development by integrating security practices into the software development lifecycle, conducting regular code reviews, and employing automated security testing tools to identify software vulnerabilities early.
Why is application security important in software development?
Application security is important in software development because it helps to protect software applications from security threats and vulnerabilities, ensuring the integrity, confidentiality, and availability of the data processed by the applications.
What are the key security practices to implement throughout the development lifecycle?
Key security practices to implement throughout the development lifecycle include threat modeling, secure coding standards, continuous integration of security tools, and regular training for developers on the latest cybersecurity measures.
How can software developers mitigate security risks in their projects?
Software developers can mitigate security risks in their projects by conducting thorough security reviews, utilizing secure frameworks and libraries, and maintaining up-to-date knowledge of emerging security threats and vulnerabilities.